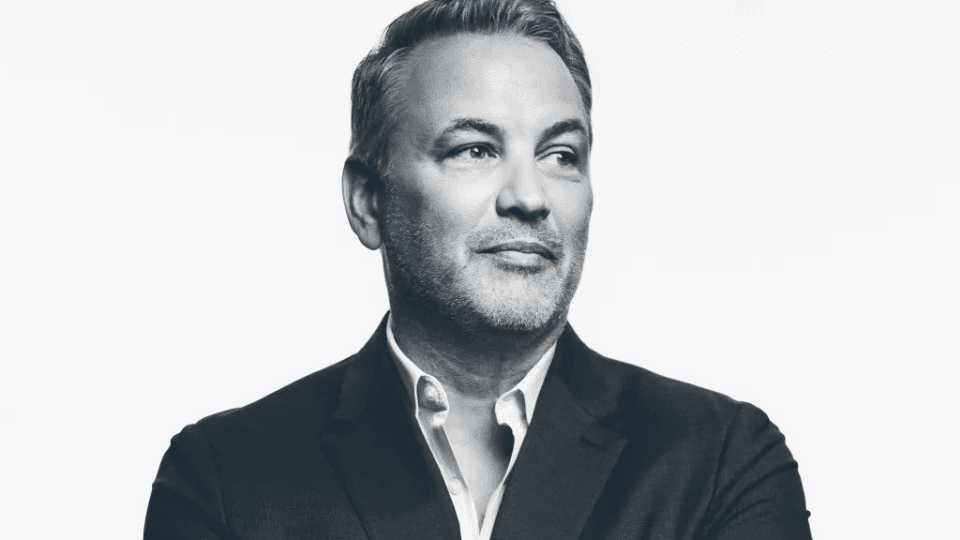
Agent Turned Investor: Ex-Secret Service Operative Raises $250 Million Cybersecurity Fund
Former Secret Service agent Bryan Seely is raising a second $250 million venture capital fund dedicated entirely to funding cybersecurity startups. Seely first gained national attention years ago after successfully hacking the United States Secret Service and the Federal Bureau of Investigation, using basic Google Maps manipulation tactics to intercept incoming phone calls to official field offices. Rather than facing federal charges, Seely turned his intelligence work into a law enforcement asset, helping agents track down cybercriminals before jumping into private venture capital investing.
Seely’s firm, Cyber Threat Capital, successfully closed its inaugural $100 million fund last year, deploying capital into early-stage security startups focused on threat detection, identity verification, and industrial network safety. The new $250 million capital vehicle expands the firm’s reach, targeting mid-stage cybersecurity platforms that protect enterprise networks, cloud data centers, and critical infrastructure systems.
The transition from intelligence enforcement to venture capital gives Seely a distinct perspective on modern threat intelligence. During his law enforcement work, Seely recruited active hackers to work alongside federal investigation teams, turning threat actors into informant sources. That hands-on experience with adversary tactics now shapes how Cyber Threat Capital evaluates prospective startup founders, software architecture, and defensive security products.
Securing capital for dedicated cybersecurity funds comes at a pivotal time for enterprise software markets. Ransomware attacks, supply chain intrusions, and social engineering scams continue to hit major corporations and government agencies worldwide. As bad actors deploy automated tools to target enterprise networks, corporate IT teams must adopt specialized defensive software to monitor endpoints, isolate cloud workloads, and safeguard sensitive databases.
Cyber Threat Capital focuses its investment strategy on startups building practical defense tools rather than speculative tech trends. Seely emphasizes that winning security platforms must address immediate operational vulnerabilities, such as unpatched industrial control systems, stolen credential access, and unmonitored API connections. The firm plans to write initial checks ranging between $5 million and $15 million for promising cybersecurity companies, offering direct access to Seely’s global network of law enforcement contacts, intelligence advisors, and corporate security executives.
Venture capital activity across the security sector remains strong despite broader economic slowdowns in tech investing. institutional investors view cybersecurity software as essential infrastructure spending, ensuring steady demand for innovative startup products regardless of market conditions. By doubling its capital reserves with this second $250 million fund, Cyber Threat Capital positions itself as a major backer for the next generation of enterprise defense tools.
Seely’s unique background bridges the gap between active threat hunting and venture investing. Understanding how bad actors exploit system flaws enables investors to spot effective security tools before they reach wide market adoption. As digital threats grow more sophisticated, backing experienced founders who understand real-world attack vectors will play a key role in shaping future network security standards.